


FireEye Helix
本文档介绍了如何将 FireEye Helix 与 Google Security Operations 集成。
使用场景
- 提取 Trellix Helix 提醒,并使用这些提醒创建 Google Security Operations 提醒。接下来,在 Google SecOps 中,提醒可用于通过 playbook 或手动分析执行编排。
- 执行修复操作,例如将实体添加到屏蔽名单
产品权限
生成一个令牌,并将其用作每个请求的特殊标头的一部分。
GET /helix/id/hexqsj477/api/v3/appliances/health HTTP/1.1
Host: helix.eu.fireeye.com
x-fireeye-api-key: xxxxxxxxxxxxxxxxxxxxx
如何生成 API 令牌
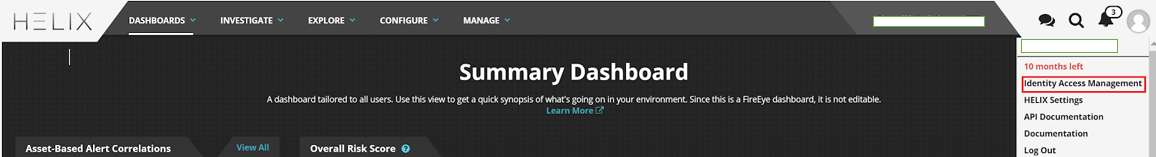
前往身份访问权限管理。
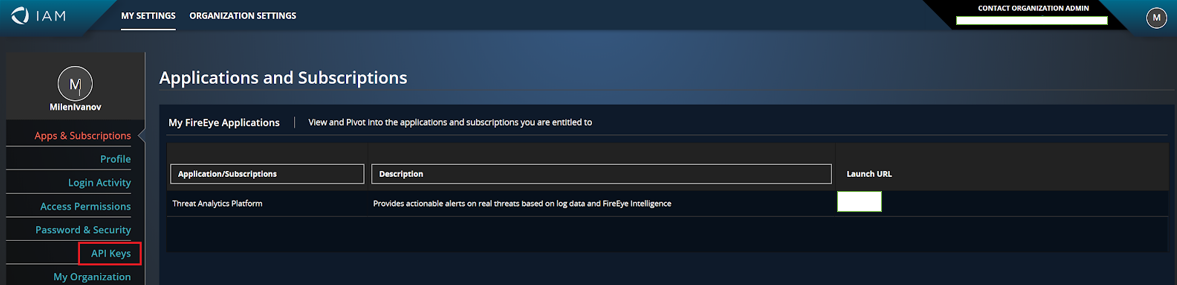
前往 API 密钥,然后点击创建 API 密钥。
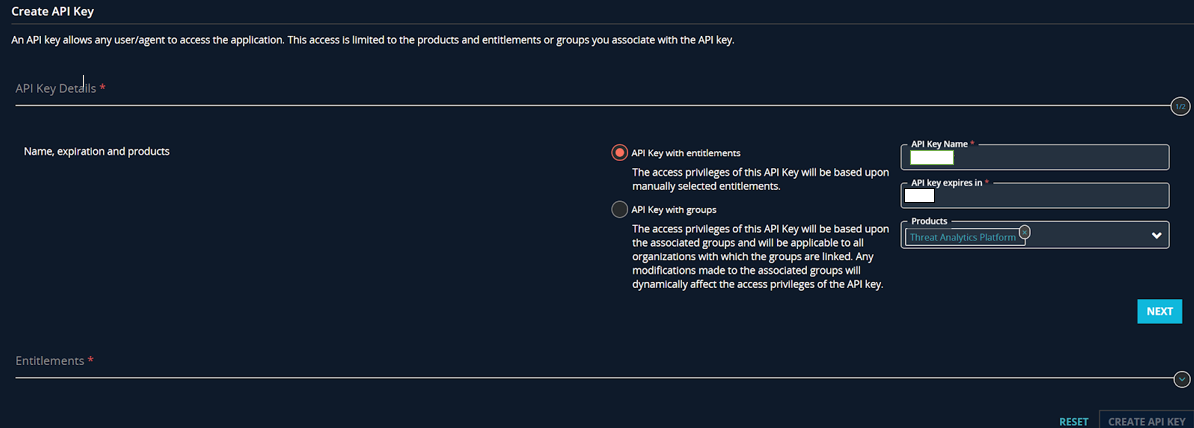
设置“API 密钥名称”“失效日期”“产品”,然后按“下一步”。
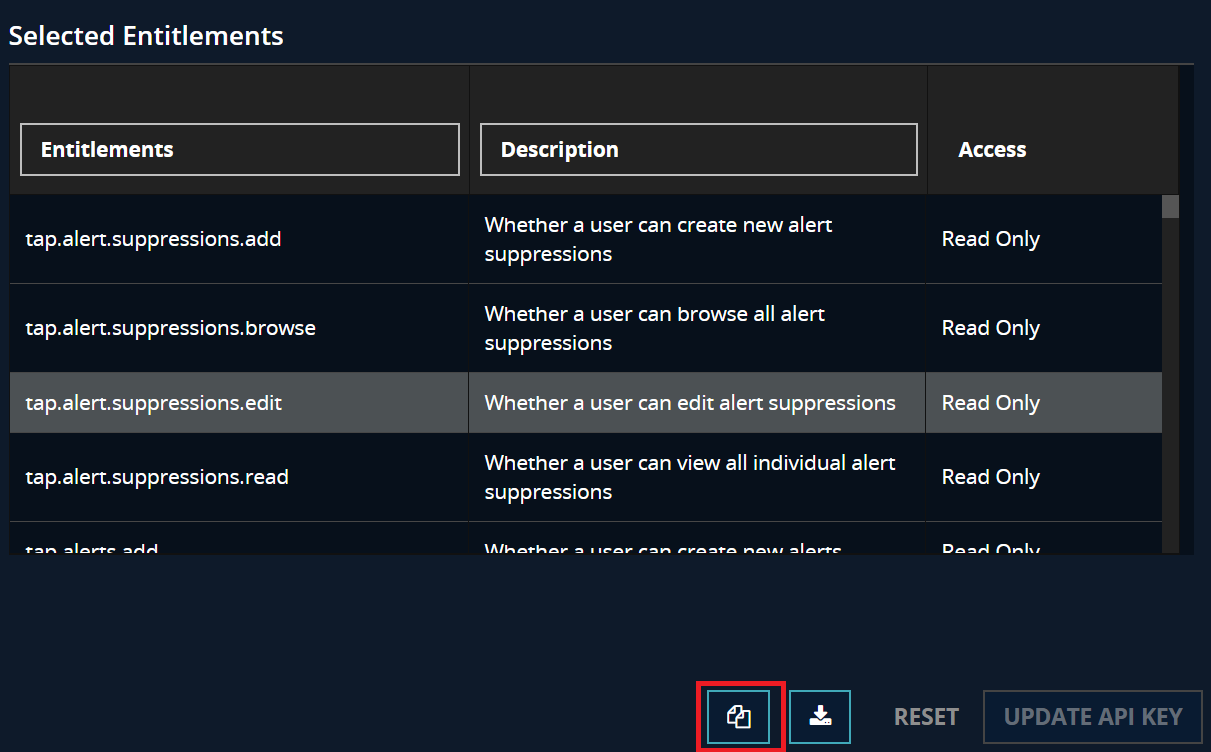
为集成添加以下权限:
- tap.alert.suppressions.add
- tap.alert.suppressions.browse
- tap.alert.suppressions.edit
- tap.alert.suppressions.read
- tap.alerts.browse
- tap.alerts.edit
- tap.alerts.read
- tap.appliances.browse
- tap.appliances.read
- tap.archivesearch.add
- tap.archivesearch.browse
- tap.assets.browse
- tap.assets.read
- tap.lists.add
- tap.lists.browse
- tap.lists.edit
- tap.lists.read
- tap.search.browse
- tap.search.regex
复制 API 令牌。
在 Google SecOps 中配置 FireEye HELIX 集成
有关如何在 Google SecOps 中配置集成的详细说明,请参阅配置集成。
集成参数
使用以下参数配置集成:
| 参数 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 实例名称 | 字符串 | 不适用 | 否 | 您要为其配置集成的实例的名称。 |
| 说明 | 字符串 | 不适用 | 否 | 实例的说明。 |
| API 根 | 字符串 | https://helix.eu.fireeye.com/helix/id/{id}/ | 是 | Trellix Helix 实例的 API 根。 |
| API 令牌 | 字符串 | 不适用 | 否 | FireEye Helix 账号的 API 令牌。 |
| 客户端 ID | 字符串 | 不适用 | 否 | 用于 Trellix IAM OAuth 身份验证的客户端 ID。 |
| 客户端密钥 | 密码 | 不适用 | 否 | 用于 Trellix IAM OAuth 身份验证的客户端密钥。 |
| 范围 | 字符串 | xdr.alr.r xdr.org.adm | 否 | 用于 Trellix IAM OAuth 身份验证的范围(以空格分隔)。 |
| 验证 SSL | 复选框 | 尚未核查 | 否 | 如果启用,则会验证与 Trellix Helix 服务器连接的 SSL 证书是否有效。 |
| 远程运行 | 复选框 | 尚未核查 | 否 | 勾选此字段,以便远程运行配置的集成。选中后,系统会显示选择远程用户(代理)的选项。 |
操作
Ping
说明
使用 Google SecOps“内容中心”页面中集成配置页面上提供的参数,测试与 Trellix Helix 的连接。
参数
不适用
Playbook 应用场景示例
该操作用于在 Google SecOps Content Hub 页面中的集成配置页面上测试连接性,并且可以作为人工处置措施执行,而不能在 playbook 中使用。
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 输出“Successfully connected to the Trellix Helix server with the provided connection parameters!” 操作应失败并停止 playbook 执行: 如果出现严重错误,例如凭据错误或连接中断: Print "Failed to connect to the Trellix Helix server! 错误为 {0}”。format(exception.stacktrace) |
常规 |
抑制提醒
说明
时长以分钟为单位。我们需要获取当前时间,并加上相关时间。创建的值将用于请求的“endDate”参数。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 提醒 ID | 整数 | 不适用 | 是 | 指定需要在 Trellix Helix 中抑制的提醒的 ID。 |
| 时长 | 整数 | 不适用 | 是 | 指定应将提醒抑制多长时间(以分钟为单位)。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果找不到提醒 ID: 输出“操作无法在 Trellix Helix 中将 ID 为 {ID} 的提醒抑制 {duration} 分钟。原因:未找到 ID 为 {ID} 的提醒。” 操作应失败并停止 playbook 执行: 如果不成功: 打印“执行‘抑制提醒’操作时出错。Reason: {0}''.format(error.Stacktrace) |
常规 |
关闭提醒
说明
在 Trellix Helix 中关闭提醒。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 提醒 ID | 整数 | 不适用 | 是 | 指定需要在 Trellix Helix 中关闭的提醒的 ID。 |
| 修订版本说明 | 字符串 | 不适用 | 否 | 指定提醒的修订备注。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果找不到提醒 ID: 输出“操作无法在 Trellix Helix 中关闭 ID 为 {ID} 的提醒。原因:未找到 ID 为 {ID} 的提醒。” 操作应失败并停止 playbook 执行: 如果不成功: 输出“执行‘关闭提醒’操作时出错。Reason: {0}''.format(error.Stacktrace) |
常规 |
为提醒添加备注
说明
在 Trellix Helix 中向提醒添加备注。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 提醒 ID | 整数 | 不适用 | 是 | 指定需要在 Trellix Helix 中抑制的提醒的 ID。 |
| 注意 | 整数 | 不适用 | 是 | 指定提醒的备注。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果找不到提醒 ID: 输出“操作无法在 Trellix Helix 中为 ID 为 {ID} 的提醒添加备注。原因:未找到 ID 为 {ID} 的提醒。” 操作应失败并停止 playbook 执行: 如果不成功: 输出“Error executing action "Add Note To Alert"。Reason: {0}''.format(error.Stacktrace) |
常规 |
获取列表
说明
返回有关 Trellix Helix 列表的信息。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 名称 | 字符串 | 不适用 | 否 | 指定名称过滤条件。 |
| 简称 | 字符串 | 不适用 | 否 | 指定简称过滤条件。 |
| 有效 | 复选框 | False | 否 | 指定操作是否应仅返回有效列表。 |
| 内部 | 复选框 | False | 否 | 指定操作是否应仅返回内部列表。 |
| 受保护 | 复选框 | False | 否 | 指定操作是否应仅返回受保护的列表。 |
| 排序方式 | DDL | 名称 可能的值: 名称 简称 创建时间 |
否 | 指定应使用哪个参数对结果进行排序。 |
| 排列顺序 | DDL | 升序 可能的值: 升序 降序 |
否 | 指定结果的排列顺序。 |
| 返回的名单数上限 | 整数 | 100 | 否 | 指定要返回的列表数量。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
"results": [
        {
            "id": 14387,
            "short_name": "siemplify_atest",
            "item_count": 0,
            "types": [],
            "created_by": {
                "id": "0b48dde7-5c81-4899-978d-793540861a42",
                "avatar": "https://secure.gravatar.com/avatar/0feb076e8da5a3dff2b62cf8e53525cd",
                "name": "xxxxxxxx",
                "username": "xxx.xxxxxx@xxxxxxxxx.xx",
                "primary_email": "xxx.xxxxxx@xxxxxxxxx.xx"
            },
            "updated_by": {
                "id": "0b48dde7-5c81-4899-978d-793540861a42",
                "avatar": "https://secure.gravatar.com/avatar/0feb076e8da5a3dff2b62cf8e53525cd",
                "name": "xxxxxxxx",
                "username": "xxx.xxxxxx@xxxxxxxxx.xx",
                "primary_email": "xxx.xxxxxx@xxxxxxxxx.xx"
            },
            "created_at": "2020-08-11T07:36:24.725168Z",
            "updated_at": "2020-08-11T07:36:24.725168Z",
            "name": "xxxxxxxx xxx",
            "type": "default",
            "description": "",
            "usage": [],
            "is_internal": false,
            "is_protected": false,
            "is_active": true,
            "hash": ""
        }
    ]
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果未找到任何列表 (is_success=false): 输出“No lists were found that match the set criteria.” 操作应失败并停止 playbook 执行: 如果不成功: 输出“执行‘获取列表’操作时出错。Reason: {0}''.format(error.Stacktrace) |
常规 |
| 案例墙 | 名称:“Trellix Helix Lists” 列:
|
常规 |
获取列表项
说明
返回有关 Trellix Helix 列表项的信息。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 列表简称 | 字符串 | 不适用 | 是 | 指定列表的简称。 |
| 值 | 字符串 | 不适用 | 否 | 为商品指定值过滤条件。 |
| 类型 | DDL | 全部 可能的值: 电子邮件 FQDN IPv4 IPv6 MD5 其他 SHA-1 |
否 | 为商品指定类型过滤条件。 |
| 排序方式 | DDL | 值 可能的值: 值 类型 风险 |
否 | 指定应使用哪个参数对结果进行排序。 |
| 排列顺序 | DDL | 升序 可能的值: 升序 降序 |
否 | 指定结果的排列顺序。 |
| 返回的项目数上限 | 整数 | 100 | 否 | 指定要返回的项数。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
"results": [
        {
            "id": 45404223,
            "value": "xxxxxxxxx.xx",
            "type": "misc",
            "risk": "Low",
            "notes": "",
            "list": 4969
        }
    ]
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果未找到列表 (is_success=false): 输出“简称"{short_name}" was not found in Trellix Helix.” 如果列表中没有内容 (is_success=false): 输出“在 Trellix Helix 中,未在简称‘{short_name}’的列表中找到任何内容。” 操作应失败并停止 playbook 执行: 如果不成功: 输出“Error executing action "Get List Items". Reason: {0}''.format(error.Stacktrace) |
常规 |
向列表中添加实体
说明
将 Google SecOps 实体添加到 Trellix Helix 列表。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 列表简称 | 字符串 | 不适用 | 否 | 指定列表的简称。 |
| 风险 | DDL | 中 可能的值: 低 中 高 严重 |
否 | 指定商品的风险。 |
| 注意 | 字符串 | 不适用 | 否 | 指定应添加到项的备注。 |
运行时间
此操作会对所有实体执行。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
{
    "id": 45417477,
    "value": "misc/email/fqdn/ipv4/ipv6/md5/shaa1aa",
    "type": "misc",
    "risk": "Critical",
    "notes": "Asd",
    "list": 14387
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功且至少添加了一个提供的实体 (is_success = true): 如果未能丰富特定实体(is_success = true): Print "Action was not able to add the following entities to the Trellix Helix list with 简称 '{0}' \n: {1}".format(List Short Name, [entity.identifier]) 如果未添加任何实体 (is_success=false): 输出“在 Trellix Helix 中,没有实体以简称“{short_name}”添加到列表中。” 操作应失败并停止 playbook 执行: 如果不成功: 输出“Error executing action "Add Entities To a List". Reason: {0}''.format(error.Stacktrace) |
常规 |
索引搜索
说明
在 Trellix Helix 中执行索引搜索。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 查询 | 字符串 | 不适用 | 是 | 指定搜索查询,例如:srcserver=172.30.202.130 |
| 时间范围 | 字符串 | 不适用 | 否 | 指定搜索的时间范围。仅支持小时和天。这是 Trellix Helix 的限制。值示例: 1d - 1 天 |
| 返回的结果数上限 | 整数 | 100 | 否 | 指定要返回的结果数量。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
"results": {
"hits": {
"hits": [
{
"_score": 0.0,
"_type": "_doc",
"_id": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"_source": {
"dstusagetype": "cdn",
"_eventid": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"srcisp": "private ip address lan",
"meta_uuid": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"srcipv4": "x.x.x.x",
"alert_version": "x.x.x.x",
"cnchost": [
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx"
],
"detect_rulenames": [
"fireeye nx alert [malware-object]"
],
"dstdomain": "xxxxxxxx.xxx",
"dstregion": "california",
"meta_ts": "2020-08-13T08:34:12.000Z",
"dstipv4": "x.x.x.x",
"meta_rule": "fireeye_cms_alert-ss-0.1.4",
"alert_product": "web mps",
"srcmac": "xx:xx:xx:xx:xx:xx",
"eventlog": "malware-object",
"eventtype": "ips",
"dstcountry": "united states of america",
"msr_ruleids": [],
"meta_alert_deviceid": "867A65B84172",
"root-infection": "19",
"dstlatitude": 37.775699615478516,
"version": "x.x.x.x",
"detect_rulematches": [
{
"confidence": "high",
"severity": "medium",
"tags": [
"fireeye",
"ids",
"helixcmsrule",
"md-none"
],
"ruleid": "1.1.2370",
"rulename": "fireeye nx alert [malware-object]",
"revision": 0
}
],
"msg": "extended",
"dstisp": "cloudflare inc.",
"dstport": 80,
"metaclass": "antivirus",
"alerturl": "https://fireeye-cm.xxxxxx.xxxxx/event_stream/events_for_bot?ma_id=166",
"md5": "47f9fdc617f8c98a6732be534d8dbe9a",
"eventid": "166",
"product": "cms",
"virus": [
"fetestevent",
"fe_ml_heuristic"
],
"devicename": "fireeye-cm.xxxxxx.xxxxx",
"dstlongitude": -122.39520263671875,
"explanation": {
"malware-detected": {
"malware": [
{
"name": "fetestevent",
"stype": "vm-bot-command",
"sid": "11111112"
},
{
"profile": "win7x64-sp1m",
"http-header": "get /appliance-test/test-infection.exe http/1.1\r\nhost: fedeploycheck.fireeye.com\r\nuser-agent: mozilla/5.0 (windows nt 10.0; win64; x64; rv:79.0) gecko/20100101 firefox/79.0\r\naccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,*/*;q=0.8\r\naccept-language: en-us,en;q=0.5\r\naccept-encoding: gzip, deflate\r\nconnection: keep-alive\r\nupgrade-insecure-requests: 1\r\n\r\n http/1.1 200 ok\r\ndate: thu, 13 aug 2020 08:34:22 gmt\r\nserver: apache\r\nlast-modified: tue, 17 apr 2012 22:12:28 gmt\r\netag: \"40011-7000-4bde73bf74b00\"\r\naccept-ranges: bytes\r\ncontent-length: 28672\r\ncache-control: max-age=0\r\nexpires: thu, 13 aug 2020 08:34:22 gmt\r\nconnection: close\r\ncontent-type: application/octet-stream",
"submitted-at": "2020-08-13t08:32:15z",
"name": "fe_ml_heuristic",
"downloaded-at": "2020-08-13t08:34:08z",
"md5sum": "47f9fdc617f8c98a6732be534d8dbe9a",
"executed-at": "2020-08-13t08:34:12z",
"application": "windows explorer",
"sha256": "b009f4c1b52cbe6db873fd601b68735a05b0721556eea73690b704f77f04b17e",
"type": "exe",
"original": "test-infection.exe",
"stype": "malware-guard"
}
]
},
"cnc-services": {
"cnc-service": [
{
"type": "networkanomaly",
"sname": "fetestevent",
"protocol": "udp",
"port": "53",
"address": "xxx.xxxxxxx.xxx"
},
{
"type": "networkanomaly",
"sname": "fetestevent",
"protocol": "udp",
"port": "53",
"address": "xxx.xxxxxxx.xxx"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"sid": "11111112",
"type": "vmsigmatch",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~cache-control: no-cache::~~connection: keep-alive::~~pragma: no-cache::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~::~~"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"type": "networkanomaly",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~cache-control: no-cache::~~connection: keep-alive::~~pragma: no-cache::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~::~~get /appliance-test/alert.html http/1.1::~~cache-control: no-cache::~~connection: keep-alive::~~pragma: no-cache::~~user-agent: winhttp example/1.0::~~host: mil.fireeye.com::~~::~~"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"sid": "11111112",
"type": "vmsigmatch",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~connection: keep-alive::~~cache-control: no-cache::~~pragma: no-cache::~~::~~"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"type": "networkanomaly",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~connection: keep-alive::~~cache-control: no-cache::~~pragma: no-cache::~~::~~get /appliance-test/alert.html http/1.1::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~connection: keep-alive::~~cache-control: no-cache::~~pragma: no-cache::~~::~~"
}
]
},
"anomaly": "229888",
"analysis": "binary"
},
"vlan": 0,
"detect_ruleids": [
"1.1.2370"
],
"alert": {
"ack": "no",
"ati-data": "{\"data\": [{\"extracted_from\": \"analysis\", \"observable_type\": \"hash\", \"context_api\": {\"threat_details\": {\"av_classifications\": [{\"first_seen\": \"2020-07-26t06:28:44.000000z\", \"av_vendor\": \"third-party-1\", \"av_product\": \"external products\", \"total_malicious\": 2, \"id\": \"av-results-type--b0ea2863-a6ec-3401-8892-3ccd59c9cbd8\", \"total_scanned\": 70}]}, \"name\": \"not_attributed\", \"sample_metadata\": {\"hashes\": {\"md5\": \"47f9fdc617f8c98a6732be534d8dbe9a\"}, \"mime_type\": \"application/x-dosexec\"}, \"updated_at\": \"2020-08-04 00:15:37.000000z\", \"created_at\": \"2020-08-04 00:15:37.000000z\", \"third_party_context\": {\"av_results\": [{\"product\": \"external products\", \"scanned\": \"2020-07-26t06:28:44.000000z\", \"total_malicious\": 2, \"total_scanned\": 70}]}, \"analysis_conclusion\": \"indeterminate\", \"type\": \"malware-summary\", \"id\": \"malware-summary--1e92bab8-007a-39ec-8c85-0a8859a5793c\"}, \"observable_value\": \"47f9fdc617f8c98a6732be534d8dbe9a\"}]}",
"sc-version": "1044.170"
},
"dstcountrycode": "us",
"meta_deviceid": "86F781D434CE",
"meta_sensor": "fireeye-nx1500v",
"alert_deviceid": "867a65b84172",
"class": "fireeye_nx_alert",
"severity": "majr",
"uuid": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"sha256": "b009f4c1b52cbe6db873fd601b68735a05b0721556eea73690b704f77f04b17e",
"__metadata__": {
"received": "2020-08-13T08:34:37.000Z",
"raw_batch_id": "ff9eb053-d43f-43ef-82ec-bf8b8ca169b0",
"data_type": "passthrough",
"disable_index": false,
"dynamic_taxonomy": true,
"num_events": 1,
"source_type": "json",
"target_index": "alerts",
"batch_id": "ff9eb053-d43f-43ef-82ec-bf8b8ca169b0",
"customer_id": "hexqsj477",
"id": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"sequence_number": 0
},
"sensor": "fireeye-nx1500v",
"srcport": 52903,
"srcserver": "x.x.x.x",
"rule": [
"vm-bot-command",
"malware-guard"
],
"srcusagetype": "rsv",
"deviceid": "86f781d434ce",
"action": "notified",
"attackinfo": "get /appliance-test/test-infection.exe http/1.1\r\nhost: fedeploycheck.fireeye.com\r\nuser-agent: mozilla/5.0 (windows nt 10.0; win64; x64; rv:79.0) gecko/20100101 firefox/79.0\r\naccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,*/*;q=0.8\r\naccept-language: en-us,en;q=0.5\r\naccept-encoding: gzip, deflate\r\nconnection: keep-alive\r\nupgrade-insecure-requests: 1\r\n\r\n http/1.1 200 ok\r\ndate: thu, 13 aug 2020 08:34:22 gmt\r\nserver: apache\r\nlast-modified: tue, 17 apr 2012 22:12:28 gmt\r\netag: \"40011-7000-4bde73bf74b00\"\r\naccept-ranges: bytes\r\ncontent-length: 28672\r\ncache-control: max-age=0\r\nexpires: thu, 13 aug 2020 08:34:22 gmt\r\nconnection: close\r\ncontent-type: application/octet-stream",
"dstcity": "san francisco"
},
"_index": "alerts"
}
],
"total": 9,
"max_score": 0.0
},
"_shards": {
"successful": 27,
"failed": 0,
"skipped": 0,
"total": 27
},
"took": 4,
"timed_out": false,
"metrics": {
"load": 0.9833333333333334,
"regex": false,
"list": false,
"aggregation": false,
"subsearch": false
},
"failures": []
}
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果未成功,则命中数/总数=0 (is_success=false): 输出“未找到与查询‘{query}’相符的结果。” 操作应失败并停止 playbook 执行: 如果不成功: Print "Error executing action "Index Search". Reason: {0}''.format(error.Stacktrace) |
常规 |
Archive Search
说明
在 Trellix Helix 中执行归档搜索。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 查询 | 字符串 | 不适用 | 是 | 指定搜索查询,例如 srcserver=172.30.202.130 |
| 时间范围 | 字符串 | 不适用 | 是 | 指定搜索的时间范围。仅支持小时和天。这是 Trellix Helix 的限制。值示例: 1d - 1 天 |
| 返回的结果数上限 | 整数 | 100 | 否 | 指定要返回的结果数量。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
"results": {
"hits": {
"hits": [
{
"_score": 0.0,
"_type": "_doc",
"_id": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"_source": {
"dstusagetype": "cdn",
"_eventid": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"srcisp": "private ip address lan",
"meta_uuid": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"srcipv4": "x.x.x.x",
"alert_version": "x.x.x.x",
"cnchost": [
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx",
"xxx.xxxxxxx.xxx"
],
"detect_rulenames": [
"fireeye nx alert [malware-object]"
],
"dstdomain": "cloudflare.com",
"dstregion": "california",
"meta_ts": "2020-08-13T08:34:12.000Z",
"dstipv4": "172.65.203.203",
"meta_rule": "fireeye_cms_alert-ss-0.1.4",
"alert_product": "web mps",
"srcmac": "x:x:x:x:x:x",
"eventlog": "malware-object",
"eventtype": "ips",
"dstcountry": "united states of america",
"msr_ruleids": [],
"meta_alert_deviceid": "867A65B84172",
"root-infection": "19",
"dstlatitude": 37.775699615478516,
"version": "9.0.0.916210",
"detect_rulematches": [
{
"confidence": "high",
"severity": "medium",
"tags": [
"fireeye",
"ids",
"helixcmsrule",
"md-none"
],
"ruleid": "1.1.2370",
"rulename": "fireeye nx alert [malware-object]",
"revision": 0
}
],
"msg": "extended",
"dstisp": "cloudflare inc.",
"dstport": 80,
"metaclass": "antivirus",
"alerturl": "https://fireeye-cm.xxxxxxxxxx.xxxxx/event_stream/events_for_bot?ma_id=166",
"md5": "47f9fdc617f8c98a6732be534d8dbe9a",
"eventid": "166",
"product": "cms",
"virus": [
"fetestevent",
"fe_ml_heuristic"
],
"devicename": "fireeye-cm.xxxxxxxxxx.xxxxx",
"dstlongitude": -122.39520263671875,
"explanation": {
"malware-detected": {
"malware": [
{
"name": "fetestevent",
"stype": "vm-bot-command",
"sid": "11111112"
},
{
"profile": "win7x64-sp1m",
"http-header": "get /appliance-test/test-infection.exe http/1.1\r\nhost: fedeploycheck.fireeye.com\r\nuser-agent: mozilla/5.0 (windows nt 10.0; win64; x64; rv:79.0) gecko/20100101 firefox/79.0\r\naccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,*/*;q=0.8\r\naccept-language: en-us,en;q=0.5\r\naccept-encoding: gzip, deflate\r\nconnection: keep-alive\r\nupgrade-insecure-requests: 1\r\n\r\n http/1.1 200 ok\r\ndate: thu, 13 aug 2020 08:34:22 gmt\r\nserver: apache\r\nlast-modified: tue, 17 apr 2012 22:12:28 gmt\r\netag: \"40011-7000-4bde73bf74b00\"\r\naccept-ranges: bytes\r\ncontent-length: 28672\r\ncache-control: max-age=0\r\nexpires: thu, 13 aug 2020 08:34:22 gmt\r\nconnection: close\r\ncontent-type: application/octet-stream",
"submitted-at": "2020-08-13t08:32:15z",
"name": "fe_ml_heuristic",
"downloaded-at": "2020-08-13t08:34:08z",
"md5sum": "47f9fdc617f8c98a6732be534d8dbe9a",
"executed-at": "2020-08-13t08:34:12z",
"application": "windows explorer",
"sha256": "b009f4c1b52cbe6db873fd601b68735a05b0721556eea73690b704f77f04b17e",
"type": "exe",
"original": "test-infection.exe",
"stype": "malware-guard"
}
]
},
"cnc-services": {
"cnc-service": [
{
"type": "networkanomaly",
"sname": "fetestevent",
"protocol": "udp",
"port": "53",
"address": "xxx.xxxxxxx.xxx"
},
{
"type": "networkanomaly",
"sname": "fetestevent",
"protocol": "udp",
"port": "53",
"address": "xxx.xxxxxxx.xxx"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"sid": "11111112",
"type": "vmsigmatch",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~cache-control: no-cache::~~connection: keep-alive::~~pragma: no-cache::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~::~~"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"type": "networkanomaly",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~cache-control: no-cache::~~connection: keep-alive::~~pragma: no-cache::~~user-agent: winhttp example/1.0::~~host: mil.fireeye.com::~~::~~get /appliance-test/alert.html http/1.1::~~cache-control: no-cache::~~connection: keep-alive::~~pragma: no-cache::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~::~~"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"sid": "11111112",
"type": "vmsigmatch",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~connection: keep-alive::~~cache-control: no-cache::~~pragma: no-cache::~~::~~"
},
{
"sname": "fetestevent",
"protocol": "tcp",
"url": "hxxp:///appliance-test/alert.html",
"address": "xxx.xxxxxxx.xxx",
"type": "networkanomaly",
"port": "80",
"channel": "get /appliance-test/alert.html http/1.1::~~user-agent: winhttp example/1.0::~~host: xxx.xxxxxxx.xxx::~~connection: keep-alive::~~cache-control: no-cache::~~pragma: no-cache::~~::~~get /appliance-test/alert.html http/1.1::~~user-agent: winhttp example/1.0::~~host: mil.fireeye.com::~~connection: keep-alive::~~cache-control: no-cache::~~pragma: no-cache::~~::~~"
}
]
},
"anomaly": "229888",
"analysis": "binary"
},
"vlan": 0,
"detect_ruleids": [
"1.1.2370"
],
"alert": {
"ack": "no",
"ati-data": "{\"data\": [{\"extracted_from\": \"analysis\", \"observable_type\": \"hash\", \"context_api\": {\"threat_details\": {\"av_classifications\": [{\"first_seen\": \"2020-07-26t06:28:44.000000z\", \"av_vendor\": \"third-party-1\", \"av_product\": \"external products\", \"total_malicious\": 2, \"id\": \"av-results-type--b0ea2863-a6ec-3401-8892-3ccd59c9cbd8\", \"total_scanned\": 70}]}, \"name\": \"not_attributed\", \"sample_metadata\": {\"hashes\": {\"md5\": \"47f9fdc617f8c98a6732be534d8dbe9a\"}, \"mime_type\": \"application/x-dosexec\"}, \"updated_at\": \"2020-08-04 00:15:37.000000z\", \"created_at\": \"2020-08-04 00:15:37.000000z\", \"third_party_context\": {\"av_results\": [{\"product\": \"external products\", \"scanned\": \"2020-07-26t06:28:44.000000z\", \"total_malicious\": 2, \"total_scanned\": 70}]}, \"analysis_conclusion\": \"indeterminate\", \"type\": \"malware-summary\", \"id\": \"malware-summary--1e92bab8-007a-39ec-8c85-0a8859a5793c\"}, \"observable_value\": \"47f9fdc617f8c98a6732be534d8dbe9a\"}]}",
"sc-version": "1044.170"
},
"dstcountrycode": "us",
"meta_deviceid": "86F781D434CE",
"meta_sensor": "fireeye-nx1500v",
"alert_deviceid": "867a65b84172",
"class": "fireeye_nx_alert",
"severity": "majr",
"uuid": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"sha256": "b009f4c1b52cbe6db873fd601b68735a05b0721556eea73690b704f77f04b17e",
"__metadata__": {
"received": "2020-08-13T08:34:37.000Z",
"raw_batch_id": "ff9eb053-d43f-43ef-82ec-bf8b8ca169b0",
"data_type": "passthrough",
"disable_index": false,
"dynamic_taxonomy": true,
"num_events": 1,
"source_type": "json",
"target_index": "alerts",
"batch_id": "ff9eb053-d43f-43ef-82ec-bf8b8ca169b0",
"customer_id": "hexqsj477",
"id": "e7afc97f-f3fb-4e1b-9915-a648f00b9c5f",
"sequence_number": 0
},
"sensor": "fireeye-nx1500v",
"srcport": 52903,
"srcserver": "x.x.x.x",
"rule": [
"vm-bot-command",
"malware-guard"
],
"srcusagetype": "rsv",
"deviceid": "86f781d434ce",
"action": "notified",
"attackinfo": "get /appliance-test/test-infection.exe http/1.1\r\nhost: fedeploycheck.fireeye.com\r\nuser-agent: mozilla/5.0 (windows nt 10.0; win64; x64; rv:79.0) gecko/20100101 firefox/79.0\r\naccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,*/*;q=0.8\r\naccept-language: en-us,en;q=0.5\r\naccept-encoding: gzip, deflate\r\nconnection: keep-alive\r\nupgrade-insecure-requests: 1\r\n\r\n http/1.1 200 ok\r\ndate: thu, 13 aug 2020 08:34:22 gmt\r\nserver: apache\r\nlast-modified: tue, 17 apr 2012 22:12:28 gmt\r\netag: \"40011-7000-4bde73bf74b00\"\r\naccept-ranges: bytes\r\ncontent-length: 28672\r\ncache-control: max-age=0\r\nexpires: thu, 13 aug 2020 08:34:22 gmt\r\nconnection: close\r\ncontent-type: application/octet-stream",
"dstcity": "san francisco"
},
"_index": "alerts"
}
],
"total": 9,
"max_score": 0.0
},
"_shards": {
"successful": 27,
"failed": 0,
"skipped": 0,
"total": 27
},
"took": 4,
"timed_out": false,
"metrics": {
"load": 0.9833333333333334,
"regex": false,
"list": false,
"aggregation": false,
"subsearch": false
},
"failures": []
}
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果作业暂停了 3 次 (is_success =false): 输出“未找到与归档查询‘{query}’相符的结果。原因:归档搜索作业已暂停超过 3 次。” 操作应失败并停止 playbook 执行: 如果不成功: Print "Error executing action "Archive Search". Reason: {0}''.format(error.Stacktrace) 如果时间范围参数输入有误: print "Error executing action "Archive Search". 原因:参数“时间范围”使用了意外格式。请检查指定的值。''.format(error.Stacktrace) |
常规 |
获取提醒详情
说明
从 Trellix Helix 检索有关提醒的信息。
参数
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 提醒 ID | 整数 | 不适用 | 是 | 指定需要在 Trellix Helix 中进行扩充的提醒的 ID。 |
| 返回的备注数上限 | 整数 | 50 | 否 | 指定要返回的关联备注数量。 |
运行时间
该操作不会对实体执行,也没有强制性输入参数。
操作执行结果
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
{
    "alerts": [
        {
            "_assignedAt": null,
            "_assignedTo": null,
            "_createdBy": {
                "id": "abd5feae-84fc-41e9-be61-336ec358c89a",
                "avatar": "https://secure.gravatar.com/avatar/8267ad472cbc450380f270ee60d729b5",
                "name": "System User",
                "username": "system_user",
                "primary_email": "xx.xxxxx@fireeye.com"
            },
            "_updatedBy": {
                "id": "0b48dde7-5c81-4899-978d-793540861a42",
                "avatar": "https://secure.gravatar.com/avatar/0feb076e8da5a3dff2b62cf8e53525cd",
                "name": "xxxxxxxxx",
                "username": "xxx.xxxxxx@xxxxxxx.xxx",
                "primary_email": "xxx.xxxxxx@xxxxxxx.xxx"
            },
            "alertThreat": "Unknown",
            "alertType": "fireeye_rule",
            "alertTypeDetails": {
                "source": "fireeye-domain",
                "detail": {
                    "pid": 3808,
                    "result": "quarantined",
                    "lastmodifiedtime": "2020-08-17T11:18:09.274Z",
                    "processpath": "c:\\knowbe4\\rssimulator\\start.exe",
                    "confidence": "high",
                    "filename": "c:\\knowbe4\\rssimulator\\testfolder\\tests\\9\\1873917892.axp",
                    "hx_alert_id": 504,
                    "accountdomain": "xxxxxxx-xxx",
                    "method": "oas",
                    "username": "xxxxxxxxx",
                    "virus": "generic.mg.4a1aa9b759980343",
                    "agentdomain": "xxxxxx-xxx",
                    "createdtime": "2020-05-24T11:18:08.993Z",
                    "agenthostname": "xxxxxx-xxxxxx",
                    "md5": "4a1aa9b7599803432bfe85056f1dce06",
                    "sha1": "469cf073c0ffcdfd23c28d88a851b885422ab2ce",
                    "bytes": 224888,
                    "agentip": "x.x.x.x",
                    "deviceid": "86b7f11acf8d",
                    "malwaretype": "malware",
                    "lastaccessedtime": "2020-08-17T11:18:09.274Z",
                    "objecttype": "file"
                },
                "summary": {
                    "virus": "generic.mg.4a1aa9b759980343",
                    "malwaretype": "malware"
                }
            },
            "classification": 30,
            "closedState": "Unknown",
            "confidence": "Medium",
            "context": null,
            "createDate": "2020-08-17T11:30:16.863577Z",
            "customer_id": "hexqsj477",
            "description": "FireEye HX detected and quarantined malware on this system using the AV engine.",
            "displayId": 3564,
            "distinguisherKey": "js2asebmwggfxt0ahvu034~,~malware~,~generic.mg.4a1aa9b759980343~,~quarantined",
            "distinguishers": {
                "virus": "generic.mg.4a1aa9b759980343",
                "agentid": "js2asebmwggfxt0ahvu034",
                "result": "quarantined",
                "malwaretype": "malware"
            },
            "emailedAt": 737654,
            "eventCount": 1,
            "eventsThreshold": 1,
            "firstEventAt": "2020-08-17T11:29:13.124000Z",
            "lastEventAt": "2020-08-17T11:29:13.124000Z",
            "external": [],
            "externalCount": 0,
            "externalId": "",
            "id": "5f3a6a3777e949323809f5af",
            "infoLinks": [],
            "internal": [],
            "internalCount": 0,
            "isThreat": false,
            "isTuned": false,
            "killChain": [
                "5 - Installation"
            ],
            "lastSyncMs": 1597663799165,
            "message": "FIREEYE HX [Malware Prevented]",
            "notes": [],
            "notesCount": 0,
            "organization": "hexqsj477",
            "originId": "MAP_RULE",
            "queues": [
                "Default Queue"
            ],
            "revision": 0,
            "revisions": [],
            "revisionNotes": "",
            "risk": "Medium",
            "riskOrder": 2,
            "search": "class=fireeye_hx_alert eventlog=mal result=quarantined NOT srcipv4:$exclusions.global.srcipv4",
            "secondsThreshold": 60,
            "severity": "Medium",
            "sourceRevision": 0,
            "sourceUrl": "",
            "state": "Open",
            "suppressed": true,
            "tags": [
                "fireeye",
                "helixhxrule",
                "malware",
                "av",
                "md-info"
            ],
            "threatChangedAt": null,
            "threatType": 50,
            "triggerId": "1.1.2615",
            "triggerRevision": 0,
            "tuningSearch": "",
            "updateDate": "2020-09-13T07:10:25.451790Z"
        }
    ],
    "meta": {
        "count": 1,
        "previous": null,
        "offset": 0,
        "limit": 30,
        "next": null
    }
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功: 如果找不到提醒 ID: 打印“操作无法从 Trellix Helix 返回 ID 为 {ID} 的提醒的相关信息。原因:未找到 ID 为 {ID} 的提醒。” 操作应失败并停止 playbook 执行: 如果不成功: 打印“执行‘获取提醒详情’操作时出错。Reason: {0}''.format(error.Stacktrace) |
常规 |
| 案例墙 | 表名称:Notes 表列:
|
常规 |
丰富端点
说明
按主机名提取端点的系统信息。
运行时间
此操作在 Hostname 实体上运行。
操作执行结果
实体丰富化
| 扩充项字段名称 | 来源(JSON 密钥) | 逻辑 - 适用情形 |
|---|---|---|
| FEHelix_risk_score | risk_score | 当 JSON 中有此字段时 |
| FEHelix_last_event_at | last_event_at | 当 JSON 中有此字段时 |
| FEHelix_severity | 和程度上减少 | 当 JSON 中有此字段时 |
| FEHelix_status | asset_status | 当 JSON 中有此字段时 |
| FEHelix_source | 来源 | 当 JSON 中有此字段时 |
| FEHelix_events_count | events_count | 当 JSON 中有此字段时 |
| FEHelix_is_vip_asset | is_vip_asset | 当 JSON 中有此字段时 |
| FEHelix_type | asset_type | 当 JSON 中有此字段时 |
| FEHelix_name | asset_name | 当 JSON 中有此字段时 |
| FEHelix_detections_count | detections | 当 JSON 中有此字段时 |
| FEHelix_uuid | asset_uuid | 当 JSON 中有此字段时 |
| FEHelix_department | asset_department | 当 JSON 中有此字段时 |
| FEHelix_id | id | 当 JSON 中有此字段时 |
| FEHelix_os | properties/os | 当 JSON 中有此字段时 |
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
{
    "risk_score": 0,
    "last_event_at": null,
    "asset_job_title": null,
    "severity": "Low",
    "cidr_range": null,
    "asset_status": "active",
    "source": "detection",
    "created_at": "2020-09-01T22:27:05.202322+00:00",
    "events_count": 0,
    "is_vip_asset": false,
    "asset_type": "xxxx",
    "asset_name": "xx-xxxx-xxxx",
    "last_activity": "2020-09-01T22:27:05.202322+00:00",
    "detections": 0,
    "asset_uuid": "09aa70c9-f76e-4092-a3a6-040192d24231",
    "location": null,
    "properties": {
        "os": "windows 10 enterprise evaluation"
    },
    "org": "hexqsj477",
    "id": 856440,
    "asset_department": null
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功且至少有一个提供的实体已扩充 (is_success = true): 如果未能丰富特定实体(is_success = true): Print "Action was not able to enrich the following entities in Trellix Helix\n: {0}".format([entity.identifier]) 如果未丰富任何实体 (is_success=false): 输出“No entities were enriched.” 操作应失败并停止 playbook 执行: 如果不成功: 输出“执行‘丰富端点’操作时出错。Reason: {0}''.format(error.Stacktrace) |
常规 |
丰富用户
说明
从 Trellix Helix 提取用户信息。
运行时间
此操作在 User 实体上运行。
操作执行结果
实体丰富化
| 扩充项字段名称 | 来源(JSON 密钥) | 逻辑 - 适用情形 |
|---|---|---|
| FEHelix_risk_score | risk_score | 当 JSON 中有此字段时 |
| FEHelix_last_event_at | last_event_at | 当 JSON 中有此字段时 |
| FEHelix_severity | 和程度上减少 | 当 JSON 中有此字段时 |
| FEHelix_status | asset_status | 当 JSON 中有此字段时 |
| FEHelix_source | 来源 | 当 JSON 中有此字段时 |
| FEHelix_events_count | events_count | 当 JSON 中有此字段时 |
| FEHelix_is_vip_asset | is_vip_asset | 当 JSON 中有此字段时 |
| FEHelix_type | asset_type | 当 JSON 中有此字段时 |
| FEHelix_name | asset_name | 当 JSON 中有此字段时 |
| FEHelix_detections_count | detections | 当 JSON 中有此字段时 |
| FEHelix_uuid | asset_uuid | 当 JSON 中有此字段时 |
| FEHelix_department | asset_department | 当 JSON 中有此字段时 |
| FEHelix_id | id | 当 JSON 中有此字段时 |
脚本结果
| 脚本结果名称 | “值”选项 | 示例 |
|---|---|---|
| is_success | True/False | is_success:False |
JSON 结果
{
            "risk_score": 0,
            "last_event_at": null,
            "asset_job_title": null,
            "severity": "Low",
            "cidr_range": null,
            "asset_status": "active",
            "source": "detection",
            "created_at": "2020-08-25T20:26:17.694104+00:00",
            "events_count": 0,
            "is_vip_asset": false,
            "asset_type": "User",
            "asset_name": "xxxxxxxx",
            "last_activity": "2020-08-25T20:26:17.694104+00:00",
            "detections": 0,
            "asset_uuid": "066c934a-c768-4c4f-adf5-35d03e95fc95",
            "location": null,
            "properties": {},
            "org": "hexqsj477",
            "id": 1174213,
            "asset_department": null
}
案例墙
| 结果类型 | 值 / 说明 | 类型 |
|---|---|---|
| 输出消息* | 操作不应失败,也不应停止 playbook 执行: 如果成功且至少有一个提供的实体已扩充 (is_success = true): 如果未能丰富特定实体(is_success = true): Print "Action was not able to enrich the following entities in Trellix Helix\n: {0}".format([entity.identifier]) 如果未丰富任何实体 (is_success=false): 输出“No entities were enriched.” 操作应失败并停止 playbook 执行: 如果不成功: 输出“Error executing action "Enrich User". Reason: {0}''.format(error.Stacktrace) |
常规 |
连接器
FireEye Helix - 提醒连接器
说明
从 Trellix Helix 中提取提醒。
API 身份验证
API 身份验证通过 x-fireeye-api-key 标头完成,该标头包含 API 密钥。
在 Google SecOps 中配置 FireEye Helix - 提醒连接器
如需详细了解如何在 Google SecOps 中配置连接器,请参阅配置连接器。
连接器参数
使用以下参数配置连接器:
| 参数显示名称 | 类型 | 默认值 | 为必填项 | 说明 |
|---|---|---|---|---|
| 产品字段名称 | 字符串 | 产品名称 | 是 | 输入源字段名称,以便检索产品字段名称。 |
| 事件字段名称 | 字符串 | eventtype | 是 | 输入源字段名称,以检索事件字段名称。 |
| 环境字段名称 | 字符串 | "" | 否 | 描述存储环境名称的字段的名称。 如果未找到环境字段,则环境为默认环境。 |
| 环境正则表达式模式 | 字符串 | .* | 否 | 要对“环境字段名称”字段中的值运行的正则表达式模式。 默认值为 .*,用于捕获所有值并返回未更改的值。 用于允许用户通过正则表达式逻辑操作环境字段。 如果正则表达式模式为 null 或空,或者环境值为 null,则最终环境结果为默认环境。 |
| 脚本超时(秒) | 整数 | 180 | 是 | 运行当前脚本的 Python 进程的超时限制。 |
| API 根 | 字符串 | https://helix.eu.fireeye.com/helix/id/{id} | 是 | Trellix Helix 实例的 API 根。示例: https://helix.eu.fireeye.com/helix/id/aaaqsj477 |
| API 令牌 | 字符串 | 不适用 | 否 | Trellix Helix 账号的 API 令牌。 |
| 客户端 ID | 字符串 | 不适用 | 否 | 用于 Trellix IAM OAuth 身份验证的客户端 ID。 |
| 客户端密钥 | 密码 | 不适用 | 否 | 用于 Trellix IAM OAuth 身份验证的客户端密钥。 |
| 范围 | 字符串 | xdr.alr.r xdr.org.adm | 否 | 用于 Trellix IAM OAuth 身份验证的范围(以空格分隔)。 |
| 服务器时区 | 字符串 | 不适用 | 否 | 指定 Trellix Helix 服务器上设置的时区(相对于世界协调时间 [UTC])。例如 +1、-1 等。如果未指定任何内容,连接器将使用世界协调时间 (UTC) 作为默认时区。 |
| 提取风险最低 | 字符串 | 中 | 是 | 将用于提取提醒的最低风险。 可能的值: 中 高 严重 |
| 回溯的小时数上限 | 整数 | 1 | 否 | 提取提醒的小时数。 |
| 要提取的提醒数量上限 | 整数 | 50 | 否 | 每次连接器迭代要处理的提醒数量。 |
| 将白名单用作黑名单 | 复选框 | 尚未核查 | 是 | 如果启用,白名单将用作黑名单。 |
| 验证 SSL | 复选框 | 尚未核查 | 是 | 如果已启用,请验证与 Trellix Helix 服务器的连接所使用的 SSL 证书是否有效。 |
| 代理服务器地址 | 字符串 | 不适用 | 否 | 要使用的代理服务器的地址。 |
| 代理用户名 | 字符串 | 不适用 | 否 | 用于进行身份验证的代理用户名。 |
| 代理密码 | 密码 | 不适用 | 否 | 用于进行身份验证的代理密码。 |
连接器规则
代理支持
此连接器支持代理。
需要更多帮助?获得社区成员和 Google SecOps 专业人士的解答。